


Intellectual Property Governance is no longer confined to separate registration of protection rights. It functions as an integrated control framework for managing ownership, access, and commercialization rights across a company’s digital asset portfolio. When source code, customer databases, platform accounts, AI-generated materials, or trade secrets are held or controlled by employees, service providers, or partners, the enterprise may lose authority over its assets, suffer reduced investment value, and face Intellectual Property ownership disputes.
A strong governance system allows businesses to identify assets, allocate permissions, preserve audit trails, and establish evidence of ownership for Intellectual Property assets. This framework becomes a strategic foundation for protecting competitive advantages that Long Phan Consulting helps enterprises structure, strengthen, and sustain.

Key legal notes:
Enterprises face severe exposure to losing exclusive control over their critical digital assets even while maintaining active day-to-day operations of their corporate websites, CRM networks, social media fanpages, core source codes, or internal databases. These operational vulnerabilities rarely originate from external cyber attacks alone; instead, they routinely stem from underlying employment agreements lacking explicit ownership clauses, fragmented access control protocols, and a systemic failure to preserve verifiable chain-of-title evidence.
Within the contemporary digital economy, the risk of copyright infringement must be interpreted broadly to encompass the comprehensive loss of operational control, administrative access rights, and ultimate disposal authority over an enterprise’s proprietary intellectual property. When these digital assets are left legally undefined or unstructured, foreign entities face significant hurdles in establishing definitive proof of ownership during corporate litigation, venture capital funding rounds, or cross-border M&A transactions.
The scope of an enterprise’s intellectual property assets now extends far beyond traditional registrations such as trademarks, corporate logos, marketing copy, graphics, or software packages. The modern corporate digital ecosystem encompasses domain names, web hosting infrastructures, advertising accounts, social media profiles, CRM systems, centralized databases, API integrations, cloud storage systems, internal prompt libraries, specialized automated workflows, and fine-tuned proprietary AI models.
Pursuant to Article 46 of the 2025 Law on Digital Technology Industry, digital assets are legally recognized as statutory property under the Civil Code, specifically defined as digital data that is created, stored, transferred, and authenticated utilizing digital technology within electronic environments. This statutory framework mandates that modern enterprises transition from passive storage management to a proactive governance model focused on enforcing absolute control over all digital property rights.
To mitigate enforcement exposure, multi-tiered organizations must systematically identify high-risk asset classifications prone to ownership disputes at an early stage, which include:
Absent a comprehensive corporate registry, an enterprise may physically possess data on a practical level without holding the requisite legal leverage to prove clear property rights. In complex technology disputes, legal and procedural advantages invariably rest with the party that maintains documented control over master administrative accounts, chronological system logs, immutable metadata, and original chain-of-title records.
A substantial portion of corporate digital asset losses occur not through sophisticated external security breaches, but because internal personnel, Chief Technology Officers (CTOs), freelance developers, or third-party marketing agencies retain primary registration or administrative control over vital corporate systems. This structural risk materializes when employment agreements, commercial service contracts, or external outsourcing frameworks omit rigorous terms governing intellectual property allocation, mandatory handover protocols, and the absolute return of digital property.
Pursuant to Point b, Clause 1, Article 86 of the Intellectual Property Law (as amended and supplemented by Point a, Clause 7, Article 71 of the 2025 Law on Science, Technology, and Innovation), organizations or individuals who invest financial capital and material resources in an author through commissioned assignments or contractual employment shall hold the primary right to register and own the resulting intellectual property, unless the contracting parties have expressly established a “contrary agreement” within their contract.
Consequently, corporate governance vulnerabilities frequently concentrate around the following operational pivot points:
Enterprises must urgently standardize digital asset ownership and assignment clauses across all employment documentation, marketing agency agreements, and technology vendor contracts. Neglecting this preventative measure allows operational control to become critically fragmented, severely diluting corporate valuation during due diligence and creating prolonged operational stalemates when attempting to reclaim critical infrastructure.
An Intellectual Property Governance system serves as a structured corporate framework enabling enterprises to identify, classify, regulate, and legally validate ownership over their intellectual property, digital assets, and AI implementations. The operational focus of IP Governance extends far beyond filing isolated protection applications; it establishes comprehensive control over the entire asset lifecycle—ranging from original creation, secure storage, and commercial exploitation to multi-tiered access authorization and enforcement protocols.
For technology firms, marketing agencies, e-commerce platforms, or rapidly expanding franchise models, a robust IP Governance framework directly dictates an organization’s capacity to protect proprietary data, safely optimize commercial monetization, and seamlessly pass rigorous technology legal due diligence during venture funding rounds or M&A transactions.
Enterprises must systematically audit and inventory their intangible assets based on specific legal classifications, distinct protection mechanisms, and operational risk profiles. This precise categorization forms the baseline for determining which assets require formal statutory registration, which demand absolute confidentiality, and which necessitate restricted access control.
| Asset Classification | Typical Examples | Core Governance Mechanism | Non-Compliance Exposure Risks |
| Traditional Intellectual Property | Registered trademarks, corporate logos, software applications, raw source code, proprietary training manuals, creative copy, and commercial graphics. | Formal statutory registration, rigorous documentation of creation history, and structured licensing or usage agreements. | Unauthorized third-party duplication, costly copyright ownership disputes, and severe dilution of core brand equity. |
| Digital Assets | Corporate domain names, official websites, marketing ad managers, social fanpages, CRM platforms, customer databases, cloud repositories, and API integrations. | Explicit verification of the corporate registration entity, centralized administrative access control, automated backups, and real-time user log tracking. | Complete loss of system access, administrative account hijacking, and hostaging of critical operational data by third parties. |
| AI Assets | Curated model training datasets, custom prompt libraries, proprietary internal automation workflows, corporate chatbots, and fine-tuned foundational models. | Immutable logging of prompt histories, strict verification of input data legality, and human-in-the-loop approval mechanisms for generated outputs. | Inability to establish legal property rights, systemic corporate data leakage, and third-party infringement liability. |
| Digital Trade Secrets | Proprietary backend algorithms, underlying data structures, specialized AI workflows, custom operational scoring models, and automated business processes. | Non-Disclosure Agreements (NDAs), multi-factor access segmentation, end-to-end data encryption, and continuous log auditing. | Unlawful misappropriation by former personnel or competitors, and an inability to legally substantiate actual material damages in court. |
Pursuant to Clause 23, Article 4 of the 2005 Intellectual Property Law (as amended and supplemented in 2022), a trade secret is legally defined as information obtained from financial or intellectual investment activities that remains undisclosed and is capable of providing a competitive advantage in business operations. Consequently, proprietary backend algorithms, unique generative AI workflows, or automated operational scoring models constitute core enterprise assets, provided the organization actively enforces verifiable, substantive confidentiality measures.
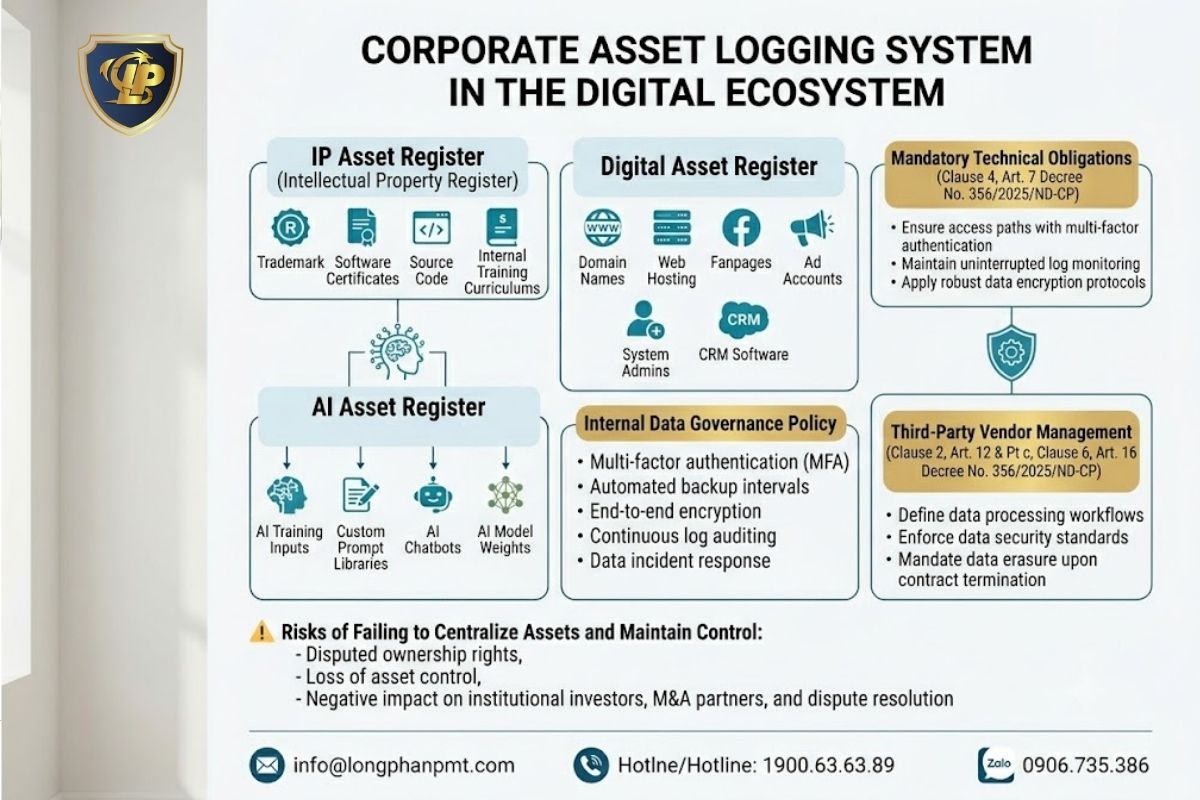
To safeguard corporate value, modern enterprises must transition from fragmented file storage management to a holistic, ecosystem-driven asset governance model. While a formal IP Register legally tracks traditional intellectual property rights, a distinct Digital Asset Register documents operational control over domain names, platform accounts, structural data networks, corporate AI frameworks, and root administrative permissions.
A standard corporate governance framework should integrate the following multi-tiered logging systems and compliance policies:
When executing large-scale data processing operations or utilizing enterprise cloud environments, businesses are legally required to secure access paths through multi-factor authentication, maintain uninterrupted log monitoring, and apply robust data encryption protocols both at rest and during network transmission. These mandatory technical obligations are explicitly codified under Clause 4, Article 7, as well as Points b and d, Clause 3, Article 9 of Decree No. 356/2025/ND-CP.
Furthermore, when engaging third-party cloud infrastructure providers, CRM developers, or external data processing vendors, the underlying commercial contract must meticulously define the processing workflows, enforce binding data security standards, and mandate the absolute erasure or destruction of all corporate data records upon contract termination. These requirements strictly mirror the statutory obligations outlined under Clause 2, Article 12, and Point c, Clause 6, Article 16 of Decree No. 356/2025/ND-CP.
Failing to maintain a centralized asset register and a clear access control policy strips an enterprise of its capacity to prove ownership rights when a commercial dispute occurs. The ultimate compliance threat extends far beyond basic data loss; it fundamentally paralyzes an organization’s ability to demonstrate clear chain-of-title and asset control before institutional investors, M&A partners, or judicial dispute resolution bodies.
Integrating artificial intelligence utilities allows enterprises to accelerate creative production, software engineering, and operational automation. However, if an organization fails to audit input data streams, copyright allocations, brand identity markers, and corporate accountability frameworks, AI deployment can quickly transform into a systemic legal liability within the broader IP Governance infrastructure.
The primary compliance vulnerability does not stem from the mere utilization of automated tools itself; rather, it hinges on an enterprise’s capability to legally prove that human oversight maintained definitive control over the final product, that all underlying source materials were lawfully acquired, and that the outputs do not infringe upon the intellectual property rights of third parties.
Foreign investors must not assume that all corporate articles, graphics, video materials, software codebases, or industrial layouts generated with the assistance of AI models are automatically eligible for statutory copyright protection under local law. An automated corporate output is only recognized as a legally protectable work when human authors maintain a substantial, decisive, and directive role throughout the creative and engineering process.
To successfully defend title claims, enterprises must systematically archive the following internal compliance records:
Pursuant to Clause 1 and Clause 9, Article 5a of Decree No. 17/2023/ND-CP (as amended and supplemented by Decree No. 134/2026/ND-CP), copyright protection does not arise for outputs that are entirely and automatically generated by AI systems without direct human creation.
Consequently, organizations must seamlessly embed their AI production workflows directly into their centralized IP Register and internal evidence retention systems. Failing to do so leaves AI-assisted digital assets highly vulnerable to copying by competitors, as the enterprise will lack the baseline empirical evidence required to prove human creative direction, system control, and ultimate legal ownership in a court of law.
The collection and processing of training data sets represents a high-exposure risk zone for technology developers, digital marketing firms, e-commerce platforms, and software engineers operating in Vietnam. Utilizing third-party literary works, images, audio-visual files, or protected consumer information to train internal machine learning models must be strictly governed based on data origin, explicit user consent, and authorized commercial scope.
Pursuant to Clause 5, Article 7 of the 2005 Intellectual Property Law (as amended and supplemented in 2025), alongside Articles 37a, 37b, and 37c of Decree No. 17/2023/ND-CP (as amended and supplemented by Decree No. 134/2026/ND-CP), corporate entities are permitted to extract lawfully published texts and datasets for AI research, testing, and training purposes without paying royalty fees only if the activity is strictly non-commercial, does not unreasonably prejudice the original right holders, and does not generate an output that serves as a direct market replacement for the original asset.
Crucially, if right holders have explicitly reserved their proprietary rights utilizing digital rights management (DRM) technologies or embedded metadata tags, enterprises are strictly prohibited from exploiting those data assets without an explicit commercial license.
Furthermore, when deploying artificial intelligence systems to generate, manipulate, or synthesize hyper-realistic audio files, images, or video streams that mimic actual individuals or authentic historical events (deepfakes), enterprises are under a strict statutory obligation to prominently display clear, legible transparency labels to prevent public deception. These mandatory disclosure protocols are enforced under Clause 5, Article 7, as well as Clause 3 and Clause 4, Article 11 of the 2025 Law on Artificial Intelligence.
For enterprise AI infrastructures and algorithmic models that were already actively operating prior to March 1, 2026, organizations are granted a strict transitional grace period of 12 to 18 months—depending on their specific industry classification—to fully audit and align their systems with these newly enacted transparency mandates. This timeline is governed by Clause 1 and Clause 2, Article 35 of the 2025 Law on Artificial Intelligence. Failing to timely standardize these systems risks immediate administrative shutdown orders, devastating operational disruptions, and the total write-off of internal capital invested into AI development.
In digital intellectual property disputes, enterprises rarely fail due to a lack of substantive legal rights; rather, they fail because they lack the rigorous, admissible evidence required to prove those rights in court. Centralized system logs, structural metadata, source repository commit histories, internal email threads, and immutable prompt logs frequently dictate an organization’s capability to legally substantiate its original creation history, proprietary access rights, and the exact scope of third-party infringement.
An effective infringement response strategy must extend far beyond traditional copyright enforcement methods. Modern organizations must simultaneously maintain a secure electronic evidence repository, execute rapid take-down notifications, implement access restriction protocols, and construct comprehensive damages calculations.
Data messages and electronic records hold binding evidentiary value under local civil procedure, provided an enterprise can verify the absolute integrity, continuous accessibility, and authentic origin of the data streams. Consequently, simple isolated screenshots are routinely deemed insufficient by judicial bodies unless they are accompanied by underlying system log files, structural metadata, authenticated email receipts, progressive development versions, or a formal notary vi-bang (evidential log) capturing the live network environment.
To successfully preserve title and defend assets, corporate legal departments must maintain continuous archival protocols for the following evidence groups:
Pursuant to Clause 7 and Clause 8, Article 5a of Decree No. 17/2023/ND-CP (as amended and supplemented by Decree No. 134/2026/ND-CP), when seeking protection for works involving artificial intelligence, the claimant must produce clear documentation verifying the creative process and the direct controlling role of human authors. This statutory evidence standard encompasses raw input datasets, technical configuration parameters, prompt logs, human-system interaction records, design briefs, and all intermediate iterations.
Furthermore, digital service providers operating within online environments are under a strict statutory duty to systematically store users’ verified personal information and detailed system activity logs to facilitate immediate verification and criminal investigations by competent authorities. These retention mandates are enforced under Point d, Clause 2, Article 25 of the 2025 Law on Cyber Security. Absent these automated logs, an enterprise faces extreme difficulty in legally proving instances of unauthorized account breaches, data exfiltration, or the illicit scraping of proprietary AI models by external actors.
Upon identifying instances of unauthorized content duplication, source code misappropriation, social media account hijacking, or the unlawful exploitation of proprietary database records, an enterprise must execute a structured, immediate response protocol. The primary objective is to legally isolate the breach and preserve all electronic evidence before demanding platform intervention or pursuing formal judicial remedies.
A standardized corporate enforcement procedure must integrate the following operational phases:
Pursuant to Point b, Clause 1, Article 198, alongside Clause 3, Article 198b of the Intellectual Property Law, lawful right holders maintain the explicit legal authority to demand that infringing parties instantly cease their illegal conduct and remove or permanently delete all violating materials from online platforms.
For intermediary digital service platforms, the statutory deadline to temporarily take down, block, or completely terminate public access to infringing content is strictly mandated at no later than 24 hours from the exact time of receiving a legally valid takedown request or official administrative order. This enforcement timeline is governed under Clause 1, Article 113 of Decree No. 17/2023/ND-CP (as amended and supplemented by Decree No. 134/2026/ND-CP).
If an enterprise cannot empirically calculate its exact actual material damages via lost commercial profits, verified revenue reductions, or established licensing values, the court holds the statutory discretion to award punitive civil compensation up to a maximum ceiling of VND 1 billion. This judicial mechanism is codified under Point d, Clause 1, Article 205 of the Intellectual Property Law. Consequently, a rigorous electronic evidence strategy must be fully operational long before any corporate dispute materializes in court.
Intellectual property management is not just a legal defense tool, but a strategy to clarify the value of a business to investors, M&A partners, franchisees, and financial institutions. When data rights, AI rights, source code, trademarks, and trade secrets are managed transparently, businesses have a better basis to demonstrate their commercial exploitation capabilities.
In technology due diligence, investors don’t just examine revenue or tangible assets. The focus is often on data ownership, software exploitation rights, the legality of AI training data, platform admin rights, and the ability to transfer digital assets after the transaction.
Businesses need to manage intellectual property assets in a way that facilitates valuation at the following levels:
Intellectual Property Law allows businesses to use intellectual property rights, including digital assets and AI systems, for commercial transactions, capital contributions, collateral for loans, and to enhance business value. For intellectual property rights that do not yet qualify for inclusion in financial accounting records, businesses must create a separate inventory for internal management, as stipulated in Article 8a of the 2005 Intellectual Property Law (amended and supplemented in 2025).
Therefore, IP Governance directly impacts the ability to raise capital, M&A, IPO, franchising, and technology transfer. A business with a Digital Asset Register, AI Governance Policy, and a clear record of established ownership often has a higher negotiating advantage than a business that only “holds the files” but cannot prove ownership.

Managing intellectual property in the digital environment requires a combination of intellectual property law, technology contracts, data protection, AI governance, and evidence-based strategies. Long Phan Consulting supports businesses in establishing digital asset control systems that prevent risks, protect ownership rights, and optimize commercial value.
The key advisory work areas include:
Your company can send contracts, digital asset lists, or dispute documents via email.info@longphanpmt.comOr contact Long Phan Consulting company Zalo at 0906.735.386 for a preliminary assessment of your options for protecting your rights.
Proactively establishing a comprehensive intellectual property and digital asset management system is a mandatory requirement for businesses to protect their competitive advantage in the digital economy. Complex legal situations regarding data control, transparency in AI applications, and electronic evidence storage are often major obstacles for startups and investors. Businesses need to thoroughly understand the current legal framework to optimize the value of intangible assets and minimize the risk of unnecessary disputes.
Businesses are not legally recognized as the copyright holders of content automatically generated by AI systems unless there is significant human participation. Copyright is only valid when the business can prove that humans performed actions such as setting control commands, selecting, and editing results to reflect creative intent. This regulation is stipulated in Clauses 1 and 9 of Article 5a of Decree No. 17/2023/ND-CP, as amended and supplemented by Decree No. 134/2026/ND-CP.
Businesses must standardize the ownership clauses for digital assets in all service contracts from the outset to avoid the risk of partners seizing source code or customer data. When a business invests funds and physical resources, it automatically assumes the right to register intellectual property, unless the contract stipulates otherwise that changes this ownership. This complies with Point b, Clause 1, Article 86 of the Intellectual Property Law of 2005, as amended and supplemented in 2022.
Businesses operating AI are not obligated to disclose source code, detailed algorithms, or digital trade secrets during the process of explaining their operations to regulatory authorities. Their obligations are limited to describing the functionality, input data streams, and established risk control measures to ensure security. This regulation is specifically stipulated in Point e, Clause 1, Article 14 of the Artificial Intelligence Law of 2025.
Network service providers must provide user information within a maximum of 24 hours of receiving a valid request from the cybersecurity task force. In emergency situations posing a direct threat to life or national security, this period may be shortened to a maximum of 3 hours. This requirement is stipulated in Point a, Clause 2, Article 25 of the 2025 Cybersecurity Law.
Businesses are permitted to use legally published texts and data to train AI models free of charge if this activity is purely for non-commercial research and does not create directly competing products. However, businesses are not allowed to exploit the data without authorization if the owner has established technological protection measures or affixed metadata labels reserving rights. This principle is based on Clause 5, Article 7 of the Intellectual Property Law of 2005, as amended in 2025; and Articles 37a and 37b of Decree No. 17/2023/ND-CP, as amended by Decree No. 134/2026/ND-CP.
Establishing a cohesive Intellectual Property Governance infrastructure is the single most critical baseline required for modern enterprises to retain absolute ownership, access authority, and ultimate disposal rights over their intellectual property, digital assets, and integrated AI frameworks. When proprietary source code repositories, customer CRM data networks, domain registrations, corporate platform credentials, or custom AI prompt libraries are left legally unmapped and unmonitored, an organization faces catastrophic erosion of its competitive edge, severely diminished valuation during M&A due diligence, and endless operational litigation.
To urgently implement a robust enterprise IP Governance framework, secure your technology contracts, and protect your digital infrastructure assets, please contact our senior advisory desk via Hotline 1900636389 for direct, high-level specialist support from Long Phan Consulting Company.
📚 This article is provided with professional consultation based on the following legal framework:


